
I’ll be honest, security was never the fun part of running a website for me. For a long time I basically ignored it. If something broke, I fixed it. If nothing broke, I didn’t think about it at all, which in hindsight was a bit silly.
And the stakes are not small anymore. A data breach now costs $4.99 million on average around the world, and in the US it’s more than double that, going by the latest breach cost findings. That’s a record. Again. It seems to set a new record pretty much every year now.
So, cybersecurity risk management. I know, it sounds like something from a boring board meeting. But stick with me for a minute, because the actual idea is simple enough that a small blog can use it just as much as a bank can.
What Is Cybersecurity Risk Management?
Put simply, you work out what could go wrong. Then you work out how bad that would be. Then you decide what you’re going to do about it, ideally before it happens and not after.
That’s basically it.
Nobody can block every attack, and anyone who says they can is selling something. So risk management in cyber security really comes down to picking your battles. You put your time and money into the stuff that’s most likely to hit you, and that would hurt the most. The rest you sort of live with.
You’ll also hear the term information security risk management. It’s more or less the same thing, honestly. The older name was a bit more about protecting data. The newer one stretches to devices, systems, and the people using them.
Risk and Threat Aren’t the Same Thing
This one confused me for a while, so I’ll spell it out. A threat is the bad thing itself. Ransomware, say, or a dodgy email.
Risk is different. It’s how likely that bad thing is to actually happen to you, combined with how much damage it would do if it did.
So a rare threat that would barely scratch you is low risk. Not worth losing sleep over. But something that’s fairly likely and could knock your business offline for a whole week? That goes right to the top. Pretty much straight away.
The Process, Which Never Really Ends
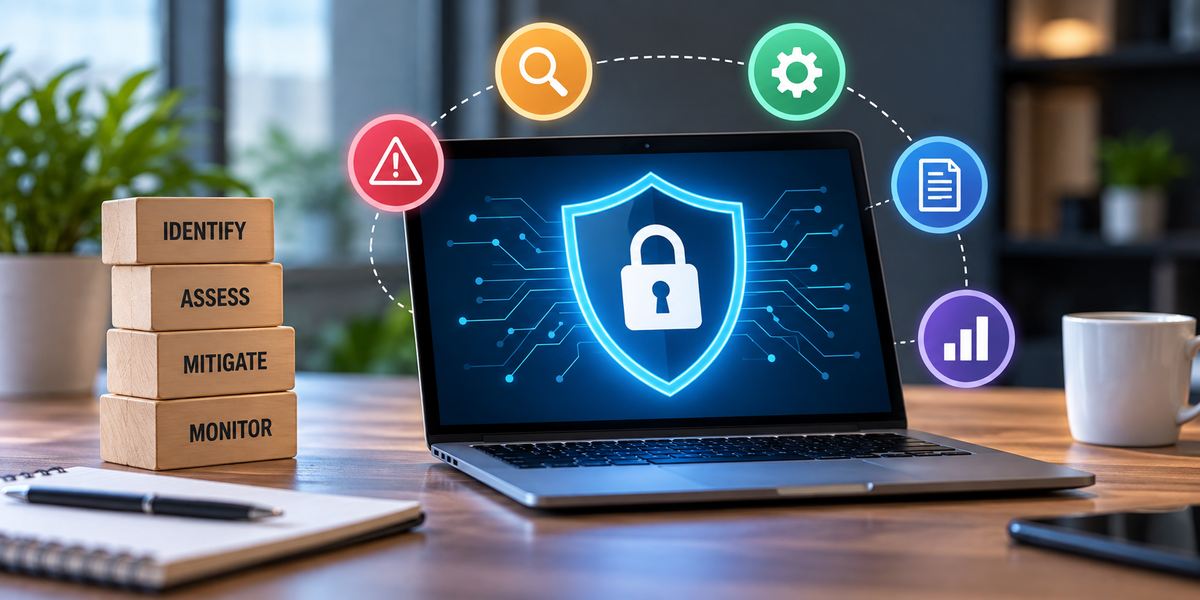
Managing cyber security risk tends to follow the same loop, whatever framework you use. The names change. The idea doesn’t.
- Figure out what you have. Every server, laptop, cloud account, and spreadsheet full of customer data. Sounds obvious. It isn’t, because almost everyone finds stuff they’d completely forgotten about.
- Work out what could go wrong. Go through each thing and ask how it could get hit. A public website has worries, like a DDoS attack, that a laptop sitting in a locked office just doesn’t.
- Decide what to do. You’ve got four options, really. Fix it, insure it, get rid of the risky thing, or shrug and accept it.
- Keep checking. New problems turn up all the time, and fixes go stale.
That fourth step? Everyone skips it. I’ve skipped it. You get everything set up, feel quite pleased with yourself, and then don’t look at it again for two years. Then something happens.
Putting a Price on It
Larger companies take it a step further and attach actual dollar amounts to each risk. There’s a method called FAIR that tries to estimate how much a given breach might cost and how often it might come up. It’s not exact. But a board will listen to “this could cost us $2 million” far more than to “this is a medium-high risk,” and that alone makes it useful.
A Couple of Frameworks Worth Knowing
You don’t need to build your own system from nothing. Other people have done that work already, thankfully.
NIST Cybersecurity Framework
The NIST Cybersecurity Framework is the big one, especially in the US. The latest version, 2.0, came out in 2024. It breaks everything into six parts: Govern, Identify, Protect, Detect, Respond, and Recover.
Govern was the new addition. I actually like that they added it, because it drags security out of the IT room and puts it in front of the people running the company. Which is where it should’ve been all along, if you ask me.
ISO 27001
ISO 27001 is the international standard. The big difference is that you can get properly certified for it, while NIST is more of a guide you follow.
A lot of companies end up going for ISO because a big customer asks for proof. So which should you start with? For most smaller businesses, I’d go with NIST. It’s easier to get into. Worry about ISO when someone actually asks you for the certificate.
Writing a Cybersecurity Risk Management Strategy
A cybersecurity risk management strategy is really just your plan, written down somewhere. It does not have to be huge. Mine, for my own site, is one page. Maybe a bit less.
What goes in it? Usually these:
- How much risk you can live with. A hospital is going to answer this very differently from a hobby blog. Obviously.
- Who owns what. Every risk needs one name next to it. “Everyone” isn’t a name, and it means nobody does anything.
- Your top few risks. Five is a good number. List them in order, plus what you’re doing about each.
- What happens when things go wrong. The first hour matters most. Who do you call? What gets switched off?
- When you’ll look at it again. Every three months works for most people.
Cyber security management, the everyday version, is just doing what that plan says. Updates, backups, checking who has access to what, and a bit of staff training. It’s dull. I won’t pretend otherwise. But dull is mostly what stops breaches.
Talk Money, Not Jargon
If you need the bosses on board, skip the technical terms. These days, boards think of cyber risk as just another business risk. What they actually want to know is how long you’d be down after an attack and what that would cost. Get those two answers ready and the budget chat gets a lot less painful.
Getting Outside Help
Plenty of companies can’t do all of this themselves. That’s normal. And there’s no shortage of people willing to help, for a price.
Services
Cybersecurity risk management services cover a lot of ground. Some are a one-time audit. Others run your whole program for you, month after month.
Cyber risk management services often throw in advice on cyber insurance too. That’s because insurers now grill you with security questions before they’ll cover you at all, so the two kind of go hand in hand these days.
If all you want is a quick picture of where you stand, a security assessment company is probably your best bet. They poke at your systems, find the weak spots, and give you a list of what to fix first. Not a bad place to start if you’re completely in the dark.
Software
On the software side, cybersecurity risk management solutions keep your risks, controls and compliance stuff in one spot. An IT risk management platform basically replaces the old spreadsheet risk register. Which, let’s be real, nobody ever kept up to date anyway.
These tools work next to your detection tools. They don’t replace them. If that part is fuzzy, it helps to understand the difference between SIEM and SOAR first.
Risk management in information technology security only really works when all these tools share information. A risk platform that never sees your actual alerts is, honestly, just a fancy to-do list.
Cybersecurity Solutions for Government
Governments have it harder. They sit on mountains of sensitive data and run services people rely on every day. Often with old systems. Usually with tight budgets.
Attackers know this. In the first half of 2026, ransomware hit government organizations about once a day, and the US made up close to a third of those. When a city gets locked out of its systems, people can’t pay bills or renew licenses. Sometimes worse.
Cybersecurity solutions for government also come with extra rules attached. Cloud providers who want to sell to US federal agencies generally need FedRAMP approval. Defense contractors have CMMC to deal with. All that slows things down, sure. But at least it sets a floor.
Cyber security solutions for government at the city or county level are a whole other story. A lot of these places don’t have a single dedicated security person. For them, the basics, like proper backups and two-step logins, do far more good than any expensive tool would.
What Comes Next
My guess is AI shakes this whole area up, both ways. Attackers already use it to write convincing phishing emails and find gaps faster. Defenders use it to sift through more alerts than any person could. I went into that back-and-forth when I wrote about how generative AI is used in cybersecurity.
The core idea won’t change, though. Know what you’ve got. Know what could go wrong. Decide what to do before it does. Old advice. Still works.