AI-generated illustration
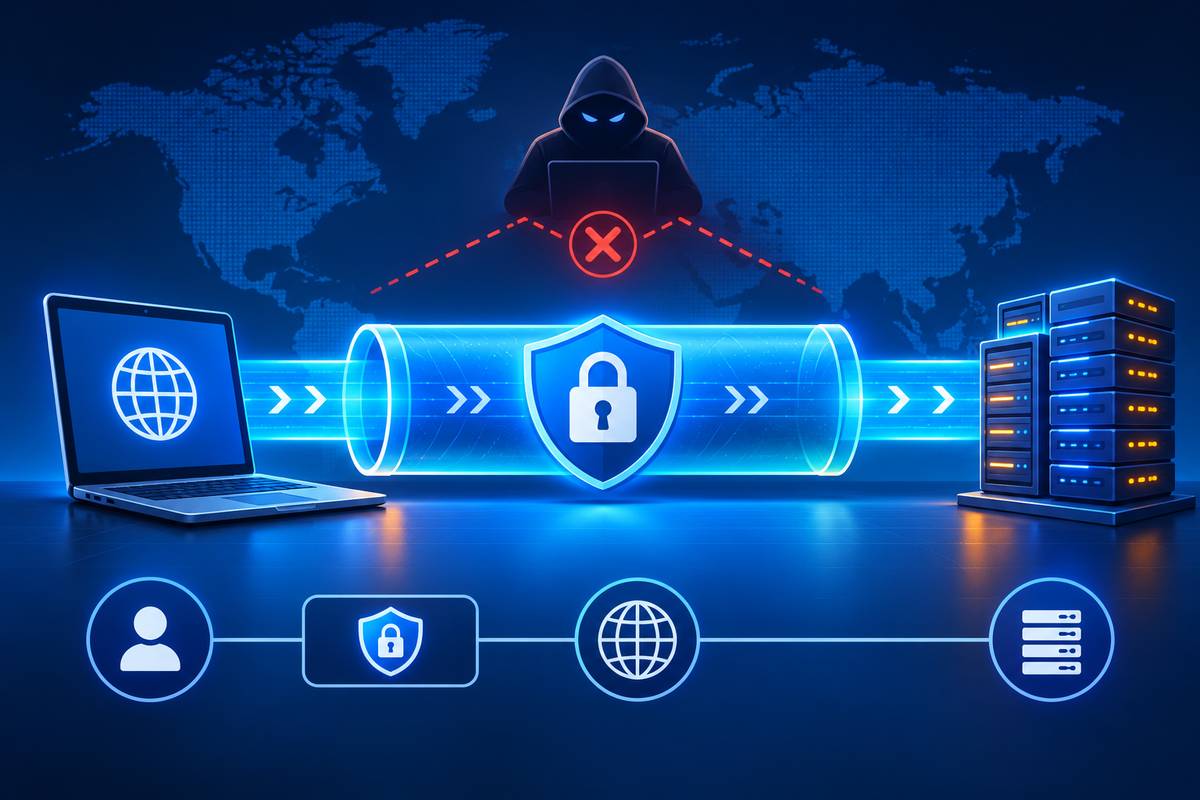
A VPN tunnel is the encrypted link between your device and a VPN server. Everything you do online goes through it, scrambled, so your internet provider can’t see what you’re up to. There’s no real tunnel, of course. It’s just encryption.
I’ve used a few VPNs over the years. TunnelBear first, then Proton VPN, and these days it’s PIA. Every time, I used them for the same boring reason: to get into sites that just wouldn’t open for me. I never really cared what a “tunnel” was. It worked, so I didn’t ask. But at some point I wanted to know what was actually going on, and that’s what this is.
What Does “VPN” Stand For?
VPN stands for virtual private network. That’s the whole acronym. The VPN definition is pretty much what the name says: a private network that runs on top of the normal internet.
Virtual, because there are no special cables. Private, because the data is encrypted. And network, because your device acts like it’s on the VPN server’s network, not yours at home.
Companies used them first, so staff could log into office systems from home. Normal people came later. Now most of us just know them as apps, and paid virtual private network services usually sell them as a monthly or yearly plan.
How Does a VPN Work, Step by Step?
A VPN wraps each piece of your data inside another, locked piece of data. That locked piece goes to the VPN server. The server opens it and sends it on to the website. Replies come back the same way.
So what is a VPN connection, in practice? It’s just this, over and over:
- The handshake. Your app and the server agree on the keys. It takes a split second.
- The wrapping. Your device puts each packet inside a new one. The new one only shows the VPN server as where it’s going.
- The locking. The inside packet gets scrambled. Nobody in the middle can tell which site you’re on.
- The unwrapping. The server opens it and passes it on with its own IP address.
That’s the tunnel. Your provider sees data going to one server, and that’s all it sees. The website sees the server, not you.
This is also why my blocked sites opened. The site didn’t see me at all. It saw a server in another country.
Why Does a VPN Slow Down Your Internet?
A VPN slows you down because every packet gets wrapped, locked and sent the long way round. More work, more distance. On every VPN I’ve used, I’ve noticed it. Not a huge drop, but pages are a little slower when it’s on.
How much depends on two things. The first is distance. A server far away will always feel slower than one close by.
The second is the protocol, which is the set of rules that builds the tunnel. And honestly, I’ve never changed mine. I’ve left PIA on whatever it picked. But the numbers say I probably should look.
WireGuard vs OpenVPN
WireGuard is newer, smaller and much faster. In one set of VPN protocol speed tests on a 1Gbps line, WireGuard got up to 950Mbps. OpenVPN mostly sat around 150 to 250Mbps. That’s a big gap.
OpenVPN isn’t useless, though. It’s been around for about 20 years, and it can run over TCP as well as UDP. That makes it harder to block on strict networks. So if WireGuard won’t connect somewhere, OpenVPN is the backup.
IKEv2, IPsec and port 4500
IKEv2 usually comes with IPsec. Phones like it because it reconnects fast when you switch from Wi-Fi to mobile data. It uses UDP port 500 to start, then port 4500 if your router uses NAT. Most home routers do.
So if you see 4500/500 in a firewall rule, that’s IPsec. Block those ports and IKEv2 won’t connect. Simple as that.
Layer 2 Tunneling Protocol and TLS VPNs
The Layer 2 Tunneling Protocol, or L2TP, doesn’t lock anything by itself. It needs IPsec for that. It’s old and slow, and I’d skip it.
TLS VPNs, also called SSL VPNs, use port 443, the same as normal secure websites. In the TLS VPN vs IPsec question, TLS is better at getting past firewalls. IPsec is usually quicker. Lots of companies use both.
Why Don’t Most VPN Servers Work?
This is the part most VPN guides skip, and it bugs me. A VPN will show you a list of 50, 80, or 100 countries. In my experience, a lot of those servers just don’t work for what you need. And I mean on paid VPNs too, not just free ones.
Some won’t connect, some connect but the site you want still blocks you, and some are so slow they may as well be off. You end up using the same three or four servers that actually work and ignoring the rest.
So when a VPN brags about server count, I don’t really care anymore. I care whether the few servers I need work every time. That’s a much shorter list, and it’s the one that matters.
What Is VPN Split Tunneling?
VPN split tunneling lets you choose which apps go through the tunnel and which use your normal internet. Anything you leave out skips the VPN. It’s mainly there for speed.
I’ll be honest, I’ve never used it. I just turn the VPN on when I need a site and off when I’m done. But I can see the point. If the VPN slows everything down, sending only one browser through it and leaving the rest alone makes a lot of sense.
Most apps have it on Windows and Android. It’s patchier on iPhone and Mac. This split tunneling guide goes through it app by app.
One catch. Anything outside the tunnel isn’t protected. That’s the trade.
VPN Tunnel on Your Phone, Router and Network
On a phone, the tunnel starts in the app. If you’ve wondered what a virtual private network on Android does, it’s the same thing, just tuned to save battery. VPNs for iOS work the same way, through the VPN settings on the iPhone.
On a router, the tunnel starts at the router and covers every device in the house. I wrote about that in my guide on what a VPN router is, since it’s the easy way to cover TVs and consoles.
Businesses go bigger. Corporate VPN solutions often link whole offices together with tunnels that stay on all the time.
Is a VPN the Same as a Proxy, VPC, or VDI?
No. They get mixed up a lot, but they’re not the same thing.
A proxy server that unblocks websites only changes your IP for one app or browser, and most of the time it doesn’t encrypt anything. A VPN covers the whole device and locks it. Free proxies are even worse. Plenty of them log what you do or stuff ads in. If you just want to unblock websites now and then, a proxy might work, but I’d never type a password through one. That’s one reason I went with a VPN in the first place.
The other two are work things. In VPC vs VPN, a VPC is a private part of a cloud network, and a VPN is how you get into it. With VDI vs VPN, VDI streams a whole desktop to you, so the files never leave the company. A VPN just connects your own device.
For teams, the best VPN for remote employees is slowly turning into a zero trust tool or a cloud-managed firewall. There’s still usually a tunnel under it, though.
Does a VPN Tunnel Make You Anonymous?
No. It hides your traffic from your provider and the Wi-Fi you’re on. But the VPN company can still see where it goes. VPN and anonymity are not the same thing.
If you use a VPN to browse anonymously, you’re trusting the VPN company not to keep logs. So pick one that has had outside audits. Check the VPN site for the actual audit reports, not just the big claims on the home page.
And if you log into Google while connected, Google knows it’s you. Tunnel or no tunnel.
What about a free VPN?
People say a free VPN is always a bad idea. I don’t fully agree. I used TunnelBear’s free plan for a while and it was good. It did what I needed. The catch is the small data allowance and fewer servers. For unblocking a site now and then, that was fine for me.
Where I’d be careful is the random free apps with no name behind them. Someone pays for those servers. Often it’s you, with your data.
How to Keep a VPN Tunnel From Leaking
A tunnel only protects you while it’s up. If the connection drops, your traffic can go straight out on the open internet, and you won’t get a warning. A kill switch stops that. It blocks all traffic until the tunnel is back.
I haven’t touched the kill switch in PIA, to be fair. Most good VPNs have one, and the Proton VPN kill switch can block all internet whenever you’re not connected. If privacy is your main reason for a VPN, I’d turn it on.
DNS leaks are the other weak spot. Your browsing can be locked while your DNS lookups still go to your provider. If lookups feel slow too, my guide on fixing slow DNS lookup has the settings to check.
Some networks block VPNs on purpose. That’s why people look up how to make a VPN undetectable. The usual answer is a “stealth” mode that makes VPN traffic look like normal web traffic.
FAQ
Yes, with a modern protocol like WireGuard, OpenVPN or IKEv2. The encryption is strong. The weak spots are leaks, old protocols like PPTP, and VPN companies that keep logs.
Yes. Websites see the VPN server’s IP, not yours. Your provider can still see that you’re using a VPN, just not what you’re doing.
Breaking modern VPN encryption isn’t realistic for normal attackers. The real problems are old VPN apps, weak passwords and leaks when the tunnel drops.
The VPN is the whole service: the app, the servers and your account. The tunnel is the locked connection it makes between your device and a server.
Where VPN Tunnels Are Headed
The tunnel idea is old, but what’s inside keeps changing. WireGuard has taken over most consumer VPNs in a few years, and companies keep adding zero trust tools on top.
What I’d really like is fewer servers that all work, instead of a hundred that mostly don’t. I’m not holding my breath.